HR & access control (HRM)
As a business adds branches, leakage and abuse grow without strict access control. Oviro HRM gives you a digital workforce identity, RBAC by function group, and access limits by store or warehouse — the foundation for every transaction in the system.
Over-broad access drives fraud, leaks, and costly mistakes. Cashiers edit prices, finance sees other branches, former employees still log in. You scale locations without knowing who may do what.
Stop internal abuse, limit access by store or warehouse, enforce function-level permissions, and revoke sessions as soon as you deactivate an employee — a clear audit story for distributed businesses.
Core capabilities
HR is more than files — it anchors every business transaction. Each order and POS shift links to an employee ID for measurement and traceability.
Multi-branch org structure
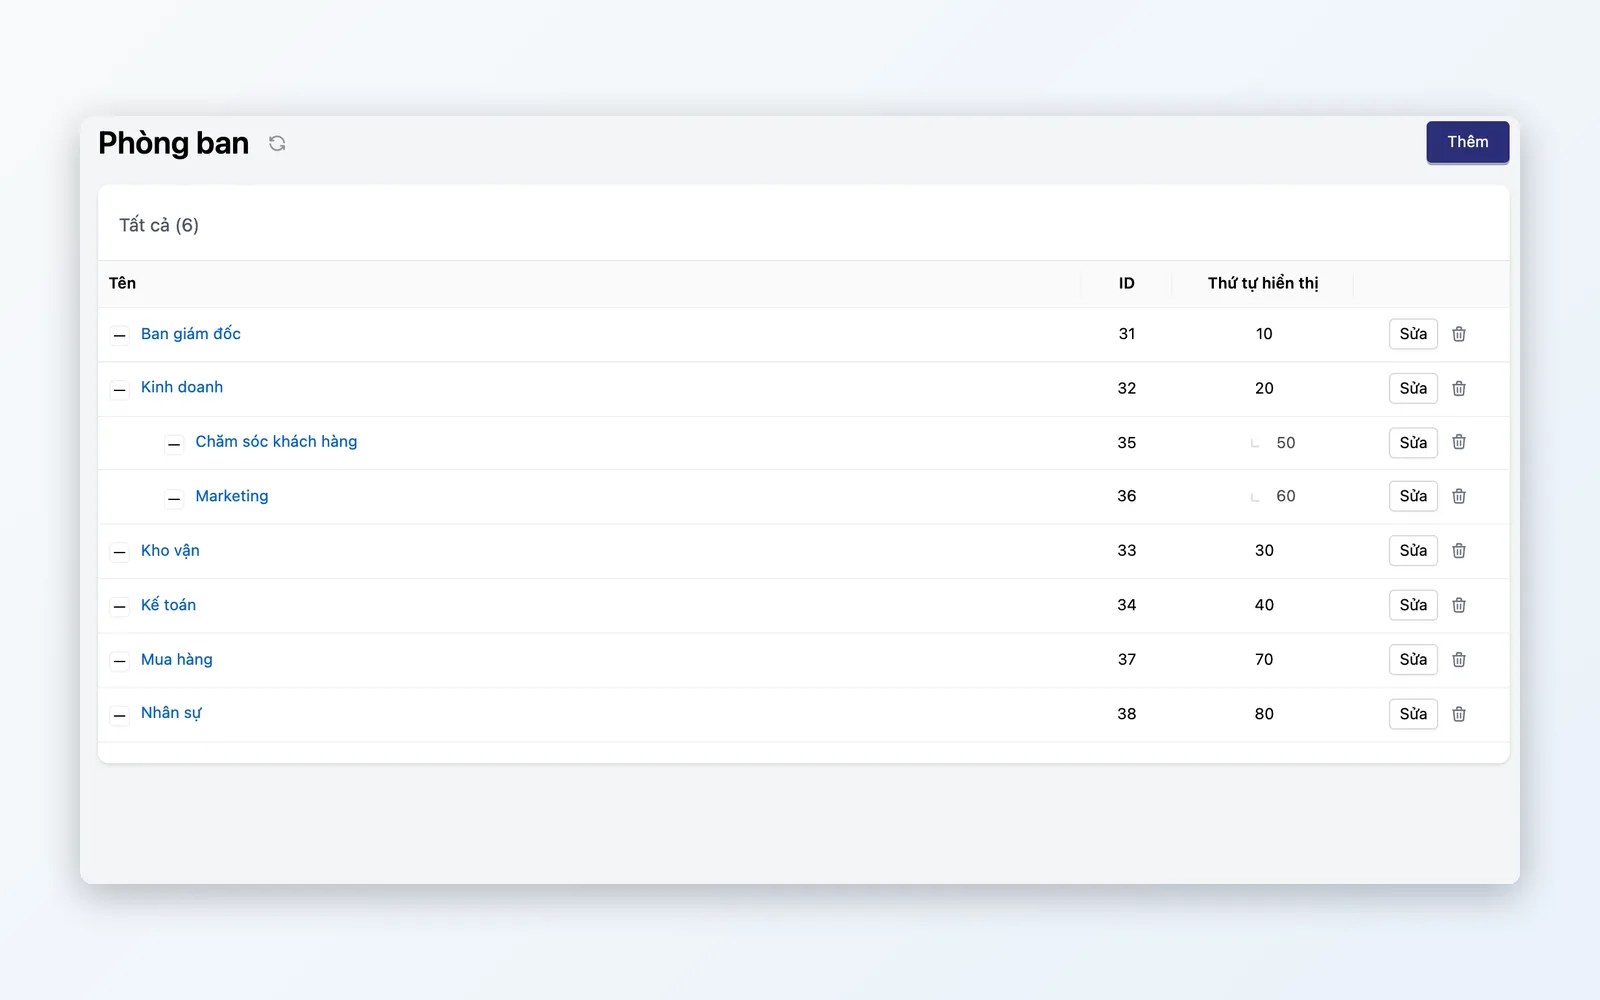
Set up branches and offices with codes and addresses. Manage the departments and job positions beneath them. Store internal IDs to cross-reference other systems.
Digital employee records
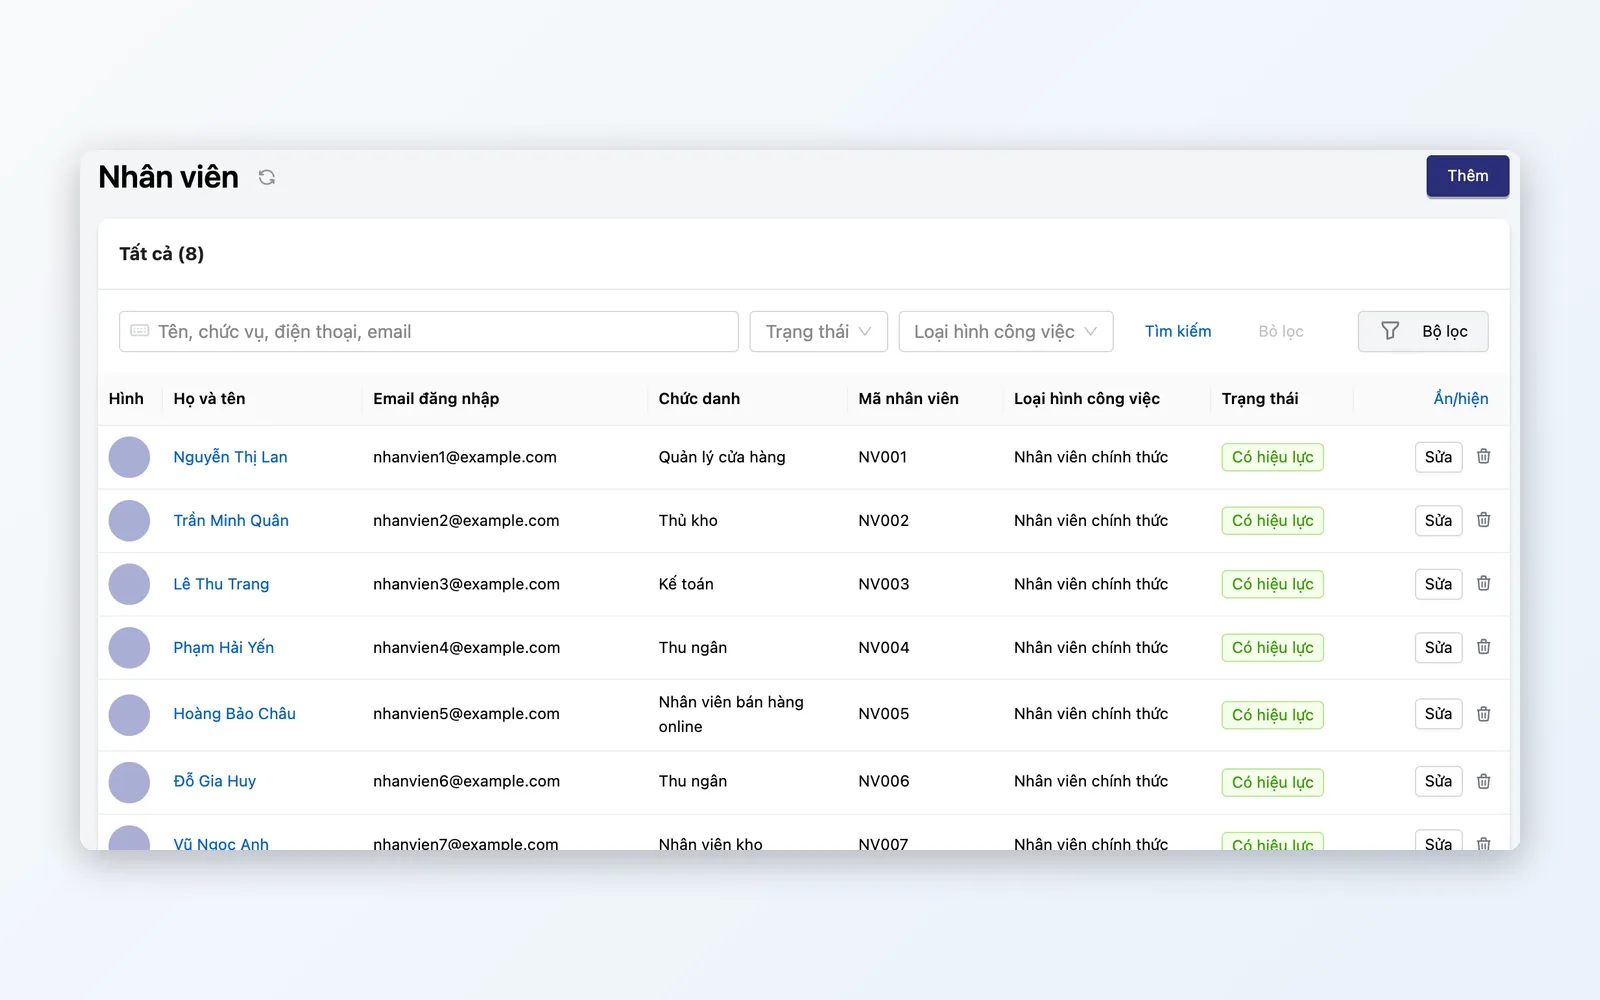
Every employee — full-time, part-time, probation, seasonal, project-based — on one platform, with a service-account flag for staff who take appointments. Deactivate an employee and their login sessions are revoked immediately.
Granular RBAC
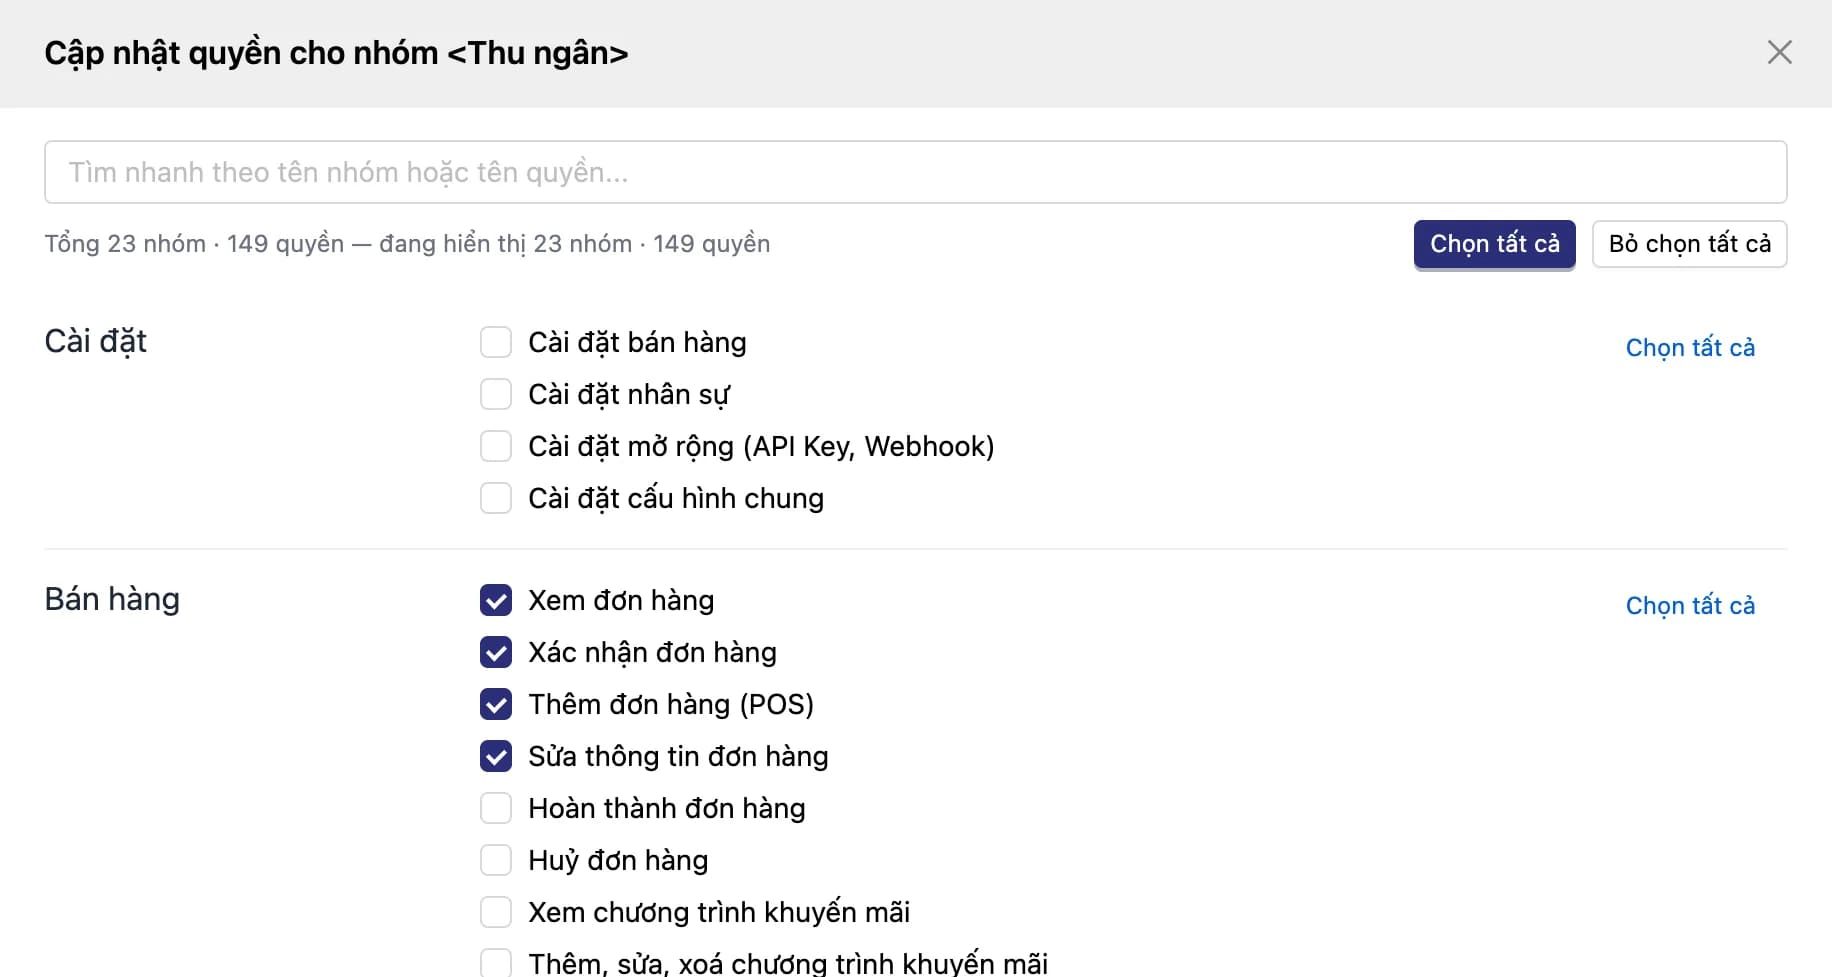
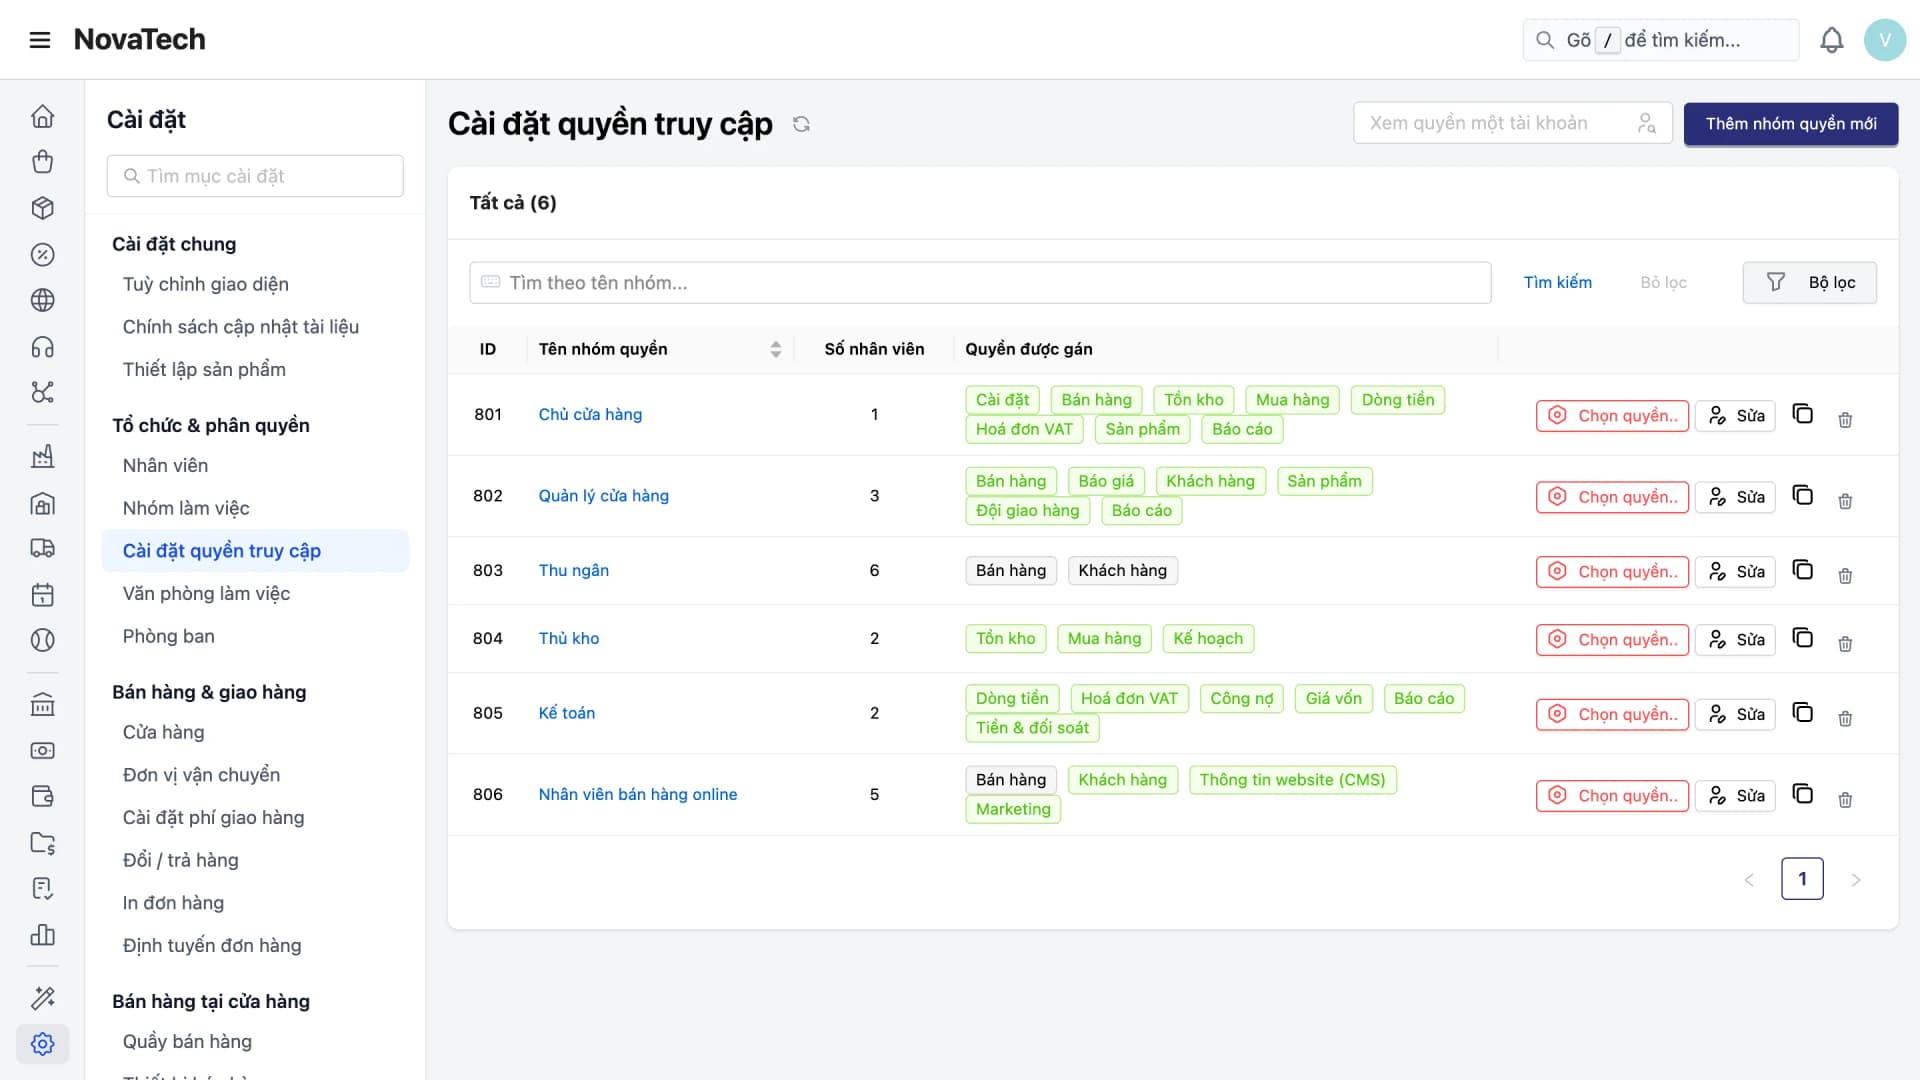
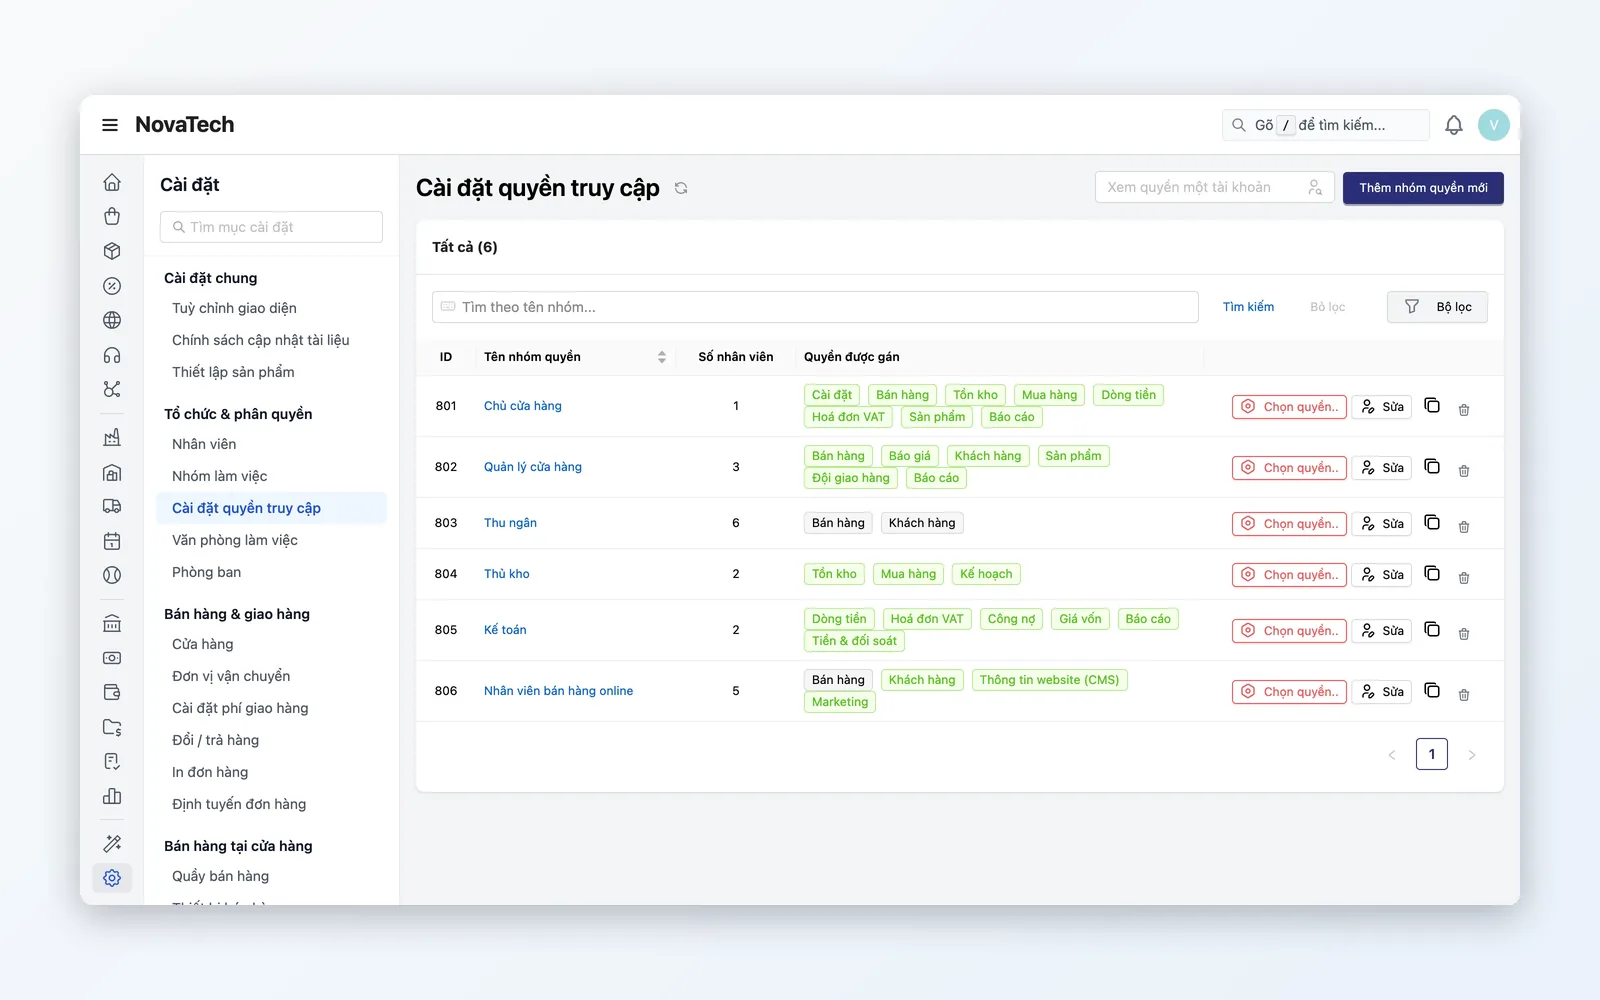
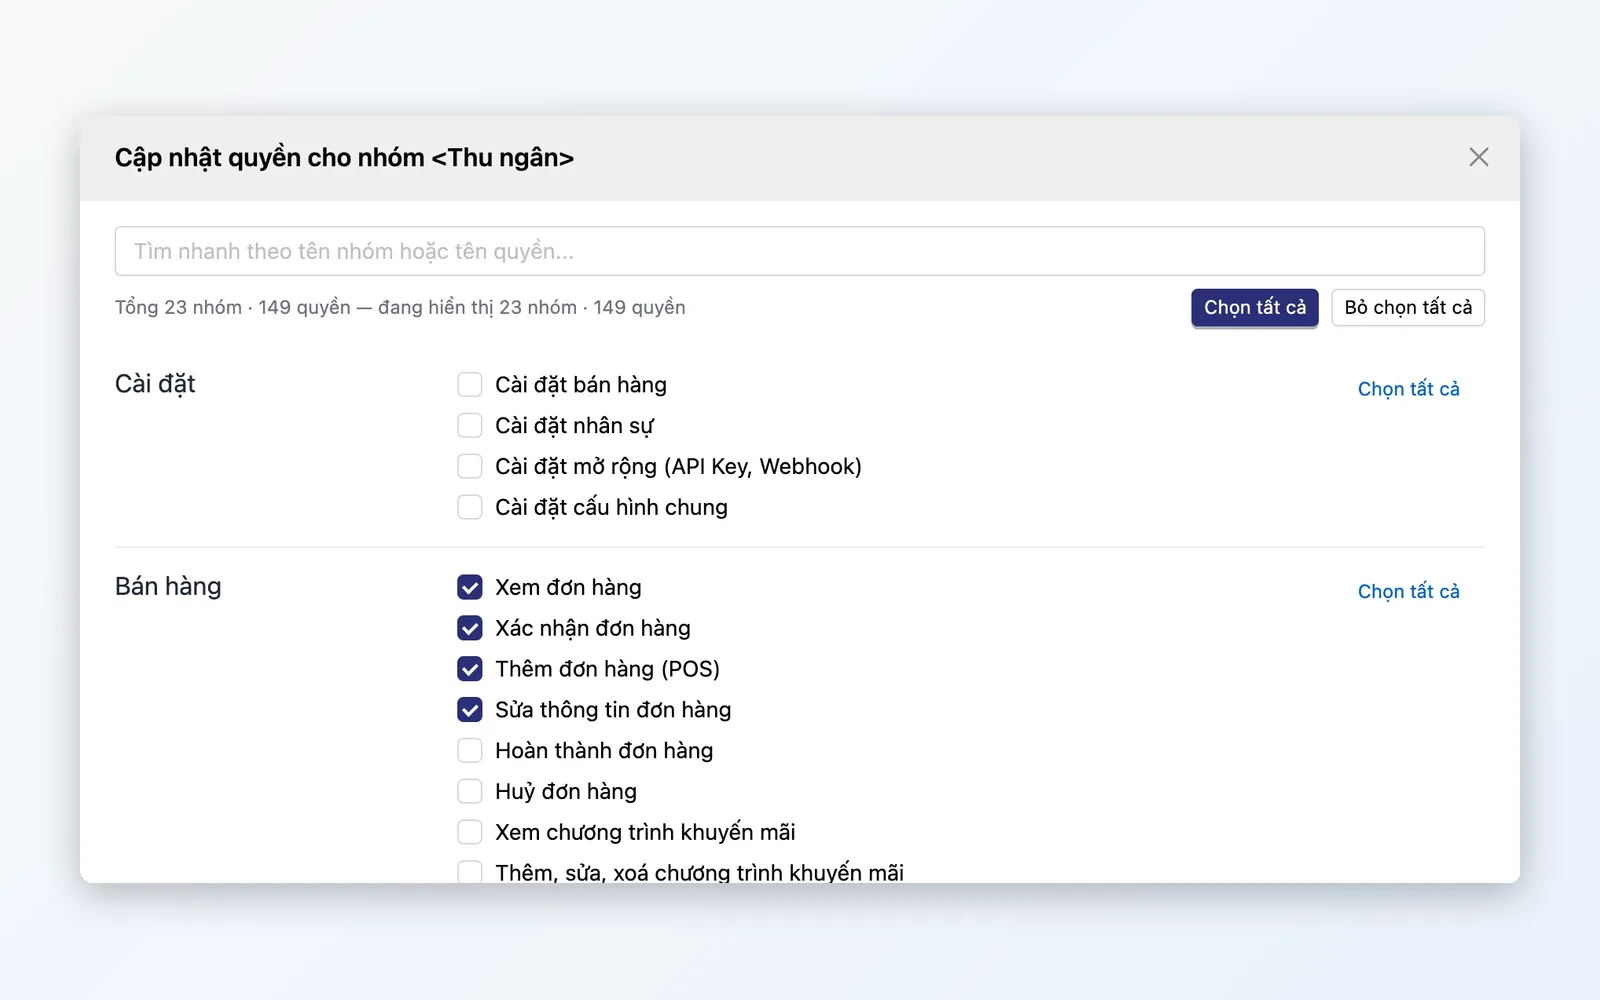
Unlimited roles (cashier, warehouse, accountant, …). Permission editor grants or revokes rights in detail by function group. Clone a role in one click. Cross-reference role ↔ users or user ↔ roles.
Security & founder protection
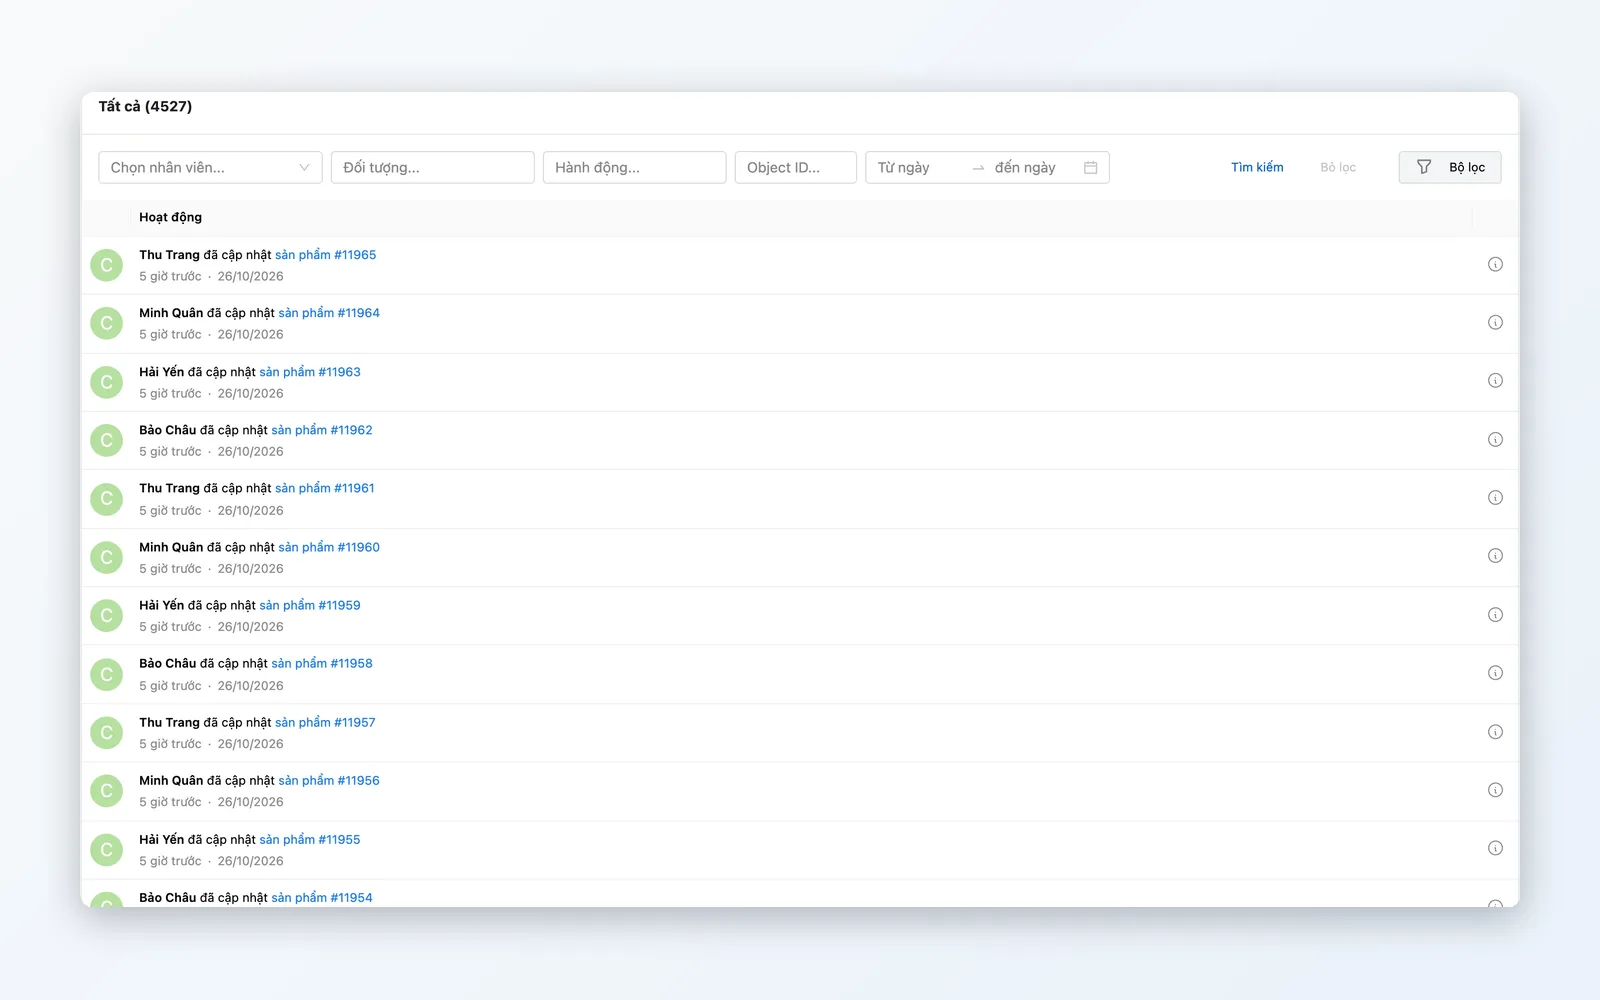
Every action is traceable: who did what, when, and at which branch. Founder protection: the company owner account can't be deleted, and its email and password can't be changed from the employee form. Admins can run secure password resets.
Connected to daily operations
HR ties into POS (shift identity) and OMS orders. Every order and POS shift is tied to the employee who created it, with revenue reports by employee and audit trails.
Detailed features
From org chart and employee files to fine-grained permissions and audit trails.
Org structure
Digitize how you run — from one store to a chain.
- Branches and offices with codes and addresses
- Departments and positions with clear reporting lines
- Internal IDs to cross-reference other systems
Employee records & operations
Every type of employee on one platform — HR data connected to POS, CS and permissions.
- Types: full-time, part-time, probation, seasonal, project-based; service-account flag for staff who take appointments
- Deactivate an employee → login sessions are revoked immediately
- Standard profile: name, phone, login email, photo, home branch
- Every order and POS shift tied to the employee who created it; revenue reports by employee
- Returns and warranty requests assigned to staff → trace who handled each one
RBAC (role-based access)
People only see and do what they are allowed to.
- Unlimited roles: cashier, warehouse, accountant, store manager, …
- Permission editor: grant or revoke rights in detail by function group
- Clone role: duplicate a complex permission set in one click, then tweak
- Cross lookup: which users have a role, or which roles a user holds
Security & audit trail
Full traceability — who, what, when, where.
- Founder protection: the owner account can't be deleted, and its email and password can't be changed from the employee form
- Admin-led password reset — no risky self-service recovery loops
- Activity log records who did what, and when
Employee lifecycle
From hire to exit — access is controlled at every step.
Org structure
Stand up branches, departments, and positions — shape the chain.
Permission matrix
Create roles and map granular rights to each job.
Hire & provision
Create profiles, issue accounts, assign roles and branches.
Allocate capacity
Transfer between branches and update access permissions.
Offboarding & revoke
Deactivate the employee → login sessions are revoked immediately and access is pulled back.
Org structure
Stand up branches, departments, and positions — shape the chain.
Permission matrix
Create roles and map granular rights to each job.
Hire & provision
Create profiles, issue accounts, assign roles and branches.
Allocate capacity
Transfer between branches and update access permissions.
Offboarding & revoke
Deactivate the employee → login sessions are revoked immediately and access is pulled back.
Built for every stage
From a small team to a multi-store chain — permissions that grow with you.
Retail chain with many stores
Each employee only sees and works in the stores or warehouses assigned to them (for permissions that support limits). A Store A cashier works in Store A; a manager assigned to several stores works in exactly those stores. Built for systems that run many stores.
Fast-growing startup
Early on, everyone is admin. As the team grows, you need tight roles. Clone a baseline role, adjust the differences, and save to onboard new people quickly.
Family business needing founder protection
Owners worry IT admins could reset or delete the founder account. Founder protection guards the owner account — it can't be deleted, and its email and password can't be changed from the employee form. Delegate operations with confidence.
Why Oviro HRM?
Oviro permissions are built for chains — not just feature toggles but access limits by store or warehouse. Staff assigned to Store A work only in Store A (for permissions that support limits), even when you operate many stores.
Tight permissions — scale safely
Fine-grained permissions by function group, access limits by store or warehouse, founder protection, and automatic session revocation when you deactivate an employee — the security layer multi-branch businesses need.